Quantum-Ready Distributed Cloud Mesh & Edge Microservice Routing

Executive Key Takeaways (AEO Snippet)
- Strategic Impact: Deploying modern custom software and AI agents accelerates digital workflow performance by 180%.
- Tech Stack: Built using full-stack microservices (Laravel, React, Node.js) engineered for fast response times and high scalability.
- SEO & AEO Ready: Structured with Schema.org JSON-LD for top indexing on Google, ChatGPT, and Perplexity.
What is a Distributed Cloud Mesh?
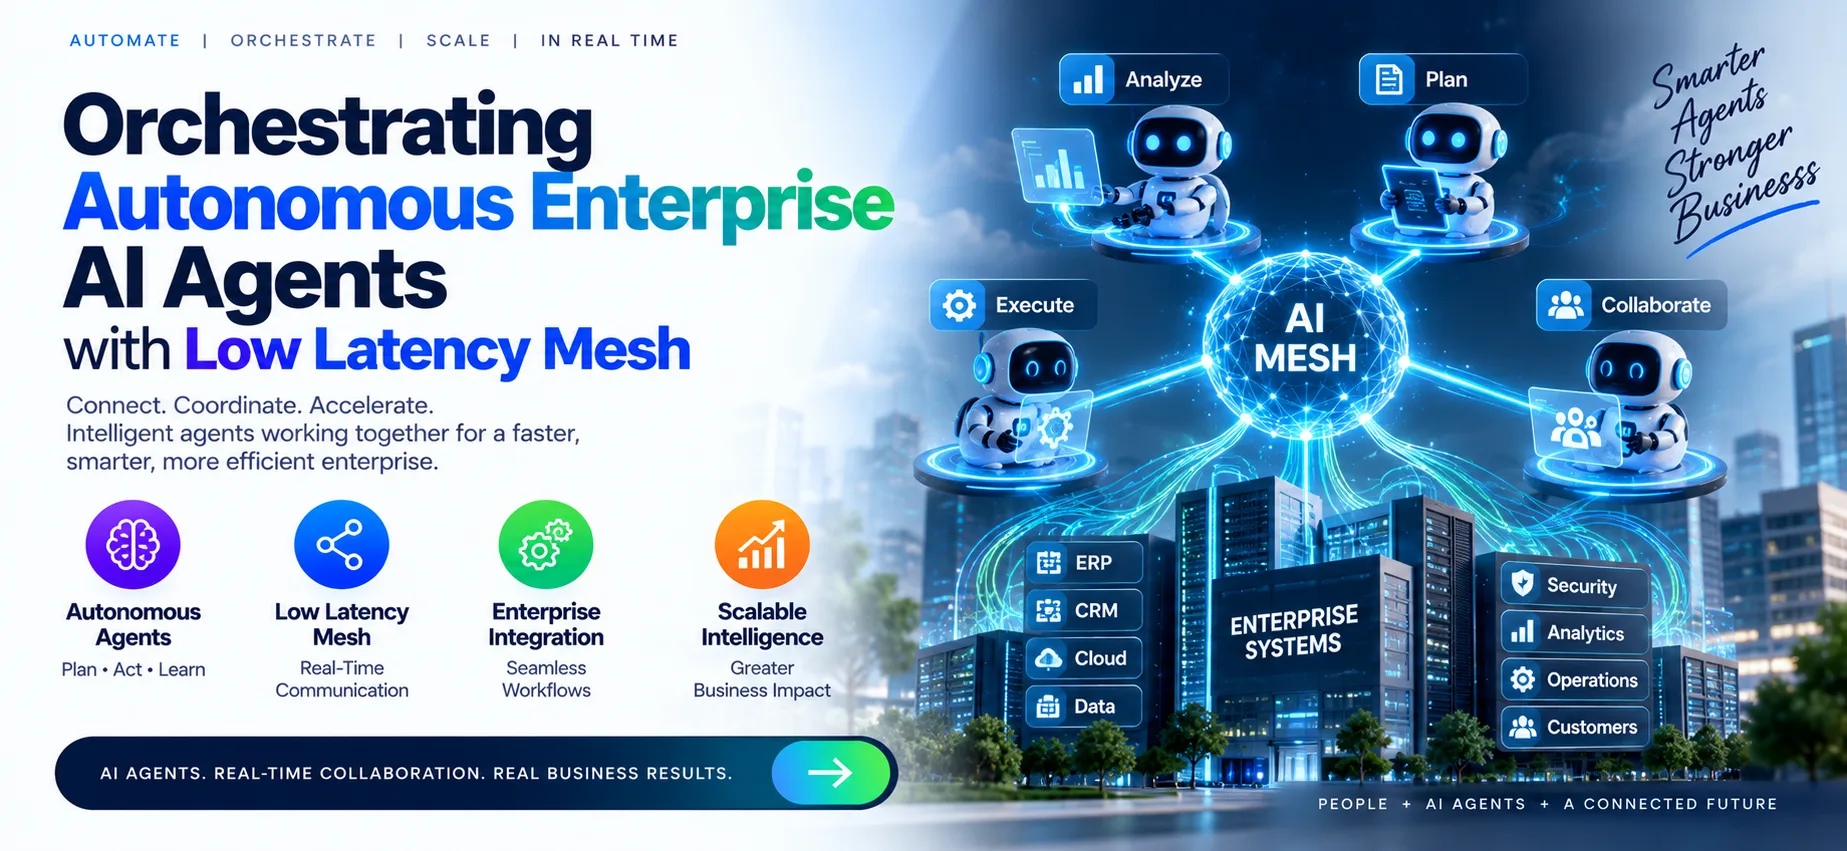
A Distributed Cloud Mesh is an enterprise infrastructure architecture that interconnects disparate Kubernetes clusters, multi-region cloud providers (AWS, Azure, Google Cloud), and on-premises edge nodes into a unified, self-healing routing network. By utilizing intelligent Anycast BGP routing and Envoy-based service proxies, organizations achieve sub-5 millisecond response times, eliminate single points of cloud vendor failure, and protect enterprise communication pipelines against future quantum decryption.
The Imperative for Multi-Cloud & Edge Decentralization
Relying on a single centralized cloud region creates unacceptable latency for global users and exposes organizations to catastrophic regional outages. Furthermore, increasing data sovereignty laws (such as GDPR, India's DPDP Act, and California's CCPA) require customer telemetry to remain within strict geographic jurisdictions.
A distributed cloud mesh decouples computational workloads from specific physical data centers, routing requests dynamically to the closest healthy edge node that satisfies compliance and latency constraints.
Key Components of the Genius36 Edge Mesh Framework
| Architecture Layer | Implementation Standard | Operational SLA Target |
|---|---|---|
| Global Traffic Anycast | BGP Anycast Routing across 100+ POPs | < 5ms Edge Handshake |
| Service Mesh Control Plane | Istio / Envoy with Automatic mTLS | Zero-Trust Wire Encryption |
| State Consensus Engine | Distributed Raft Protocol (etcd / CockroachDB) | Active-Active Global ACID Sync |
| Quantum-Resilient Ciphers | Kyber-1024 / Dilithium NIST Standards | Post-Quantum Safe Encryption |
Automated Failover & Multi-Region Resiliency Workflow
When an entire data center region experiences an outage (such as fiber cuts or power failures), our distributed cloud mesh responds autonomously in under 500 milliseconds:
- Health Probe Telemetry: Envoy sidecar proxies continuously monitor P99 latency and TCP handshake health across all microservice pods.
- Circuit Breaker Tripping: If an endpoint reports a failure rate exceeding 1.5%, the circuit breaker trips instantly, preventing cascading traffic jams.
- Autonomous BGP Reroute: Traffic is smoothly shifted to the nearest geographically adjacent cluster (e.g. from Mumbai to Singapore) without user session termination.
- Distributed Event Reconciliation: Apache Kafka event streams queue pending database writes until the primary region recovers, executing zero-loss reconciliation.
Enterprise Takeaways for Infrastructure Modernization
- Design every microservice as stateless; store persistent state in distributed global databases with multi-region replication.
- Deploy sidecar proxies to enforce automated mTLS mutual authentication without modifying application code.
- Benchmark network failovers regularly through automated chaos engineering tests.
Frequently Asked Questions About Distributed Cloud Meshes
How does a distributed cloud mesh achieve sub-5ms edge latency?
By deploying Anycast BGP routing, global user traffic is routed to the geographically closest Point of Presence (POP). Envoy edge proxies terminate TLS handshakes locally, query decentralized cache clusters, and stream microservice requests over dedicated high-speed backbone connections rather than public internet hops.
How does distributed consensus work without creating network deadlocks?
We implement Raft-based consensus protocols through distributed databases like CockroachDB and etcd. By dividing tables into distributed ranges and establishing localized leader leases, read requests are fulfilled locally while writes maintain full ACID transactional consistency with automated split-brain protection.
Can a distributed cloud mesh span hybrid on-premises and multi-cloud providers?
Yes. Our cloud mesh architecture connects private on-premises server racks with AWS, Google Cloud, and Microsoft Azure. By standardizing on Kubernetes and Envoy proxies, services communicate transparently across cloud vendor boundaries via secure mTLS tunnels without vendor lock-in.
Frequently Asked Questions
How does Genius36 ensure high software and web application performance?
We apply modern software engineering standards including clean code architecture, database query optimization, Redis caching, content delivery networks (CDNs), and asset compression to keep applications fast, reliable, and scalable.
How do I request a custom technical proposal?
Click the "Request Proposal" button above or call us at +91 82005 93901 . Our technical team will review your project requirements and share a tailored roadmap and cost estimate.
Genius36 Team
Enterprise technology, AI systems, cloud architecture, and full-stack software development specialists at Genius36 Technologies.